Indie game storeFree gamesFun gamesHorror games
Game developmentAssetsComics
SalesBundles
Jobs
TagsGame Engines

leafoAdmin

7,218
Posts
126
Topics
2,660
Followers
605
Following
A member registered Feb 26, 2013 · View creator page →

Creator of

Recent community posts

Admin (1 edit)

Okay the fix is deployed

  • Disqualified entries in “submitters/contributors only” jams no longer grant the user voting privileges
  • Additionally, we changed it so that at ranking time of “submitters/contributors only” jams, every vote is verified that the user who posted it still meets the voting criteria: they have an active game in the jam or they are a host or judge

The docs have also been updated to mention this: https://itch.io/docs/creators/game-jams#jam-customization/ranked-jams

Thanks for bringing this up!
Admin

Great question, I’m assuming you’re asking this about jams that use “submitter’s only” voting? I checked the code and I see that we don’t handle it well, the disqualified submitter is still allowed to rate entries, and all their votes are counted. Looking to see if we can patch this easily

Admin

I’m the person who coded the site telling you how it works. If you want to ignore that to push some conspiracy theory (that’s clearly false if you spend a second browsing the most recent games) then I’ll just close the thread. Thanks

Admin

No we don’t do anything like that. Your AI disclosure has nothing to do with any needs review status your page may get inserted into.

Admin (1 edit)

And you can’t solve the captcha for some reason? Or it’s just rejecting that you completed it? Also seems like you were able to post a top level reply right here. So it only happens when you reply to someone else?

Are you using any anonymizing services like Tor or something? Those networks are used a ton by scammers, so if you are then it could make our system more likely to flag your page or your comments for either captchas or human review.

Admin

We ask that developers use their best judgment when tagging their pages. It is not our staff’s job to tag your page, but in some cases a staff member may review your page. When I opened your page and immediately saw the images you had presented, I could tell that this content was clearly targeting a fetish audience. In my opinion, that means that you failed to tag your page accurately, and put the burden on our staff to tag your page. When it comes to adult content, we take this VERY strictly.

If it gets to the point where a staff member has to manually tag your page because you did not, then we consider it an abuse of our tagging system and may deindex your page https://itch.io/docs/creators/quality-guidelines

Thanks for understanding

Admin (3 edits)

This appears to be a fetish game, please mark it as Adult/NSFW. We ask devs to consider the intent behind their projects when setting the adult tagging, beyond just explicit graphic material. Failure to tag games appropriately for adult content can result in permanent desisting or a ban.

Pinned ReplyAdmin

I triggered a manual recalculation for you, tell me if there are still any issues.

Admin (4 edits)

We’ve made a bunch of changes to our OAuth system over the past year, mostly driven by work on the itch.io app, and they’re now documented and available for third-party apps. Here’s a summary of some of the changes we have made. You can always find the full up-to-date documentation here: https://itch.io/docs/api/oauth

Authorization code flow with PKCE

We’ve added support for the standard authorization code flow with PKCE: send response_type=code with a code_challenge, then exchange the code at POST https://api.itch.io/oauth/token.

We recommend using this for new integrations. It works with many existing OAuth 2.0 client libraries, the access token never shows up in the browser’s address bar, and if you have a backend you don’t need a JavaScript page to pull the token out of the URL hash. Browser-only apps can call the token endpoint directly, it returns CORS headers for your registered origin.

The implicit flow will remain, so existing apps don’t need to change anything.

Docs: https://itch.io/docs/api/oauth#authorization-code-flow-recommended

Games and desktop apps

A few changes to make OAuth easier from a native app:

  • Loopback redirect URIs (http://127.0.0.1:...) now match on any port. Register http://127.0.0.1:1234/callback and bind whatever port is free at runtime.
  • The redirect keeps any query string already in your redirect URI.
  • The copy/paste fallback (urn:ietf:wg:oauth:2.0:oob) works with the code flow, so what the user pastes is a short-lived code instead of an API key.

There’s a new section in the docs on what we recommend for games: https://itch.io/docs/api/oauth#games-and-native-applications

If your game is launched through the itch.io app you still don’t need any of this, add the scopes you need to your app manifest instead.

QR code login for devices

For handhelds and other devices without a browser we’ve created a new device authorization grant that can be used with a QR code to enable logging into itch.io on devices that don’t have a keyboard or web browser.

At this time, any apps that want to use this require approval from us, there’s more info about that in the docs: https://itch.io/docs/api/oauth#qr-code-login-device-authorization-grant

Scopes and API

New scopes available to OAuth apps:

  • game:view:ownership: check if the user owns one of your games (/games/:id/ownership)
  • game:view:uploads: download files for games the user owns and free games
  • collection:edit: create and edit the user’s collections, paired with the new collections API
  • profile:owned, profile:collections and game:view:rewards existed but weren’t documented, they’re listed now

Error responses

We normalzied some fields to make our OAuth integration more compatible with existing clients. An error field (invalid_grant, invalid_request) has been added alongside our errors array we’ve always returned, so OAuth client libraries can report something useful.

Additionally, when a user declines on the authorize page you’re now redirected back with error=access_denied and your state, instead of the user landing on their dashboard, so apps running a local callback server can stop waiting.

Please tell us if you encounter any issues, or would like to see more scopes or functionality added! Also if you’re building any interesting apps please do share them below, in the future we may consider adding an app directory so I’m curious to see what people are making.

Enjoy

Pinned ReplyAdmin

Just leaving this comment here to prevent people from bumping this old thread.

We revamped search in this version of the app https://itch.io/updates/itch-app-bundle-support-launch-args-and-more

  • The native sidebar app search results are only for searching within your library now
  • Any other search queries to can be opened in the in-app browser on the main site search
Admin

holy smokes

Admin (2 edits)

Thanks for the report, this is indeed a functionality change from the recent update to the rich text editor. In the meantime, there should be an “Insert video” button in the toolbar you can use to add an embed iframe without having to change to HTML mode

Edit: The old functionality is back, you can now paste iframe code to have it convert immediately

Pinned ReplyAdmin

test test hello world

Pinned ReplyAdmin

I believe we found and fixed the bug that was causing this issue. It appears to be have affecting only people who were making nested comment replies where their account session required a captcha. Please try again and tell us if you are still seeing the issue.

Admin (1 edit)

It’s coming very soon, we kicked off a project to scan architectures across all executables as part of our “itch donk” project. Filters for the browse page will be rolled out in the near future

Pinned ReplyAdmin (1 edit)

You have a picture of a naked real life woman in your screenshots. Please make sure you read the rules.

I’m closing this thread since there appears to be a lot of other people trying to jump in with their own issues. Please create your own topic if you need help, do not re-use other people’s topics for account related restrictions of visibility issues.

Pinned ReplyAdmin

Please don’t post NSFW content on our community forums. You account has a visibility restriction applied to it due to previous content violations. Only support can resolve your issue.

Admin

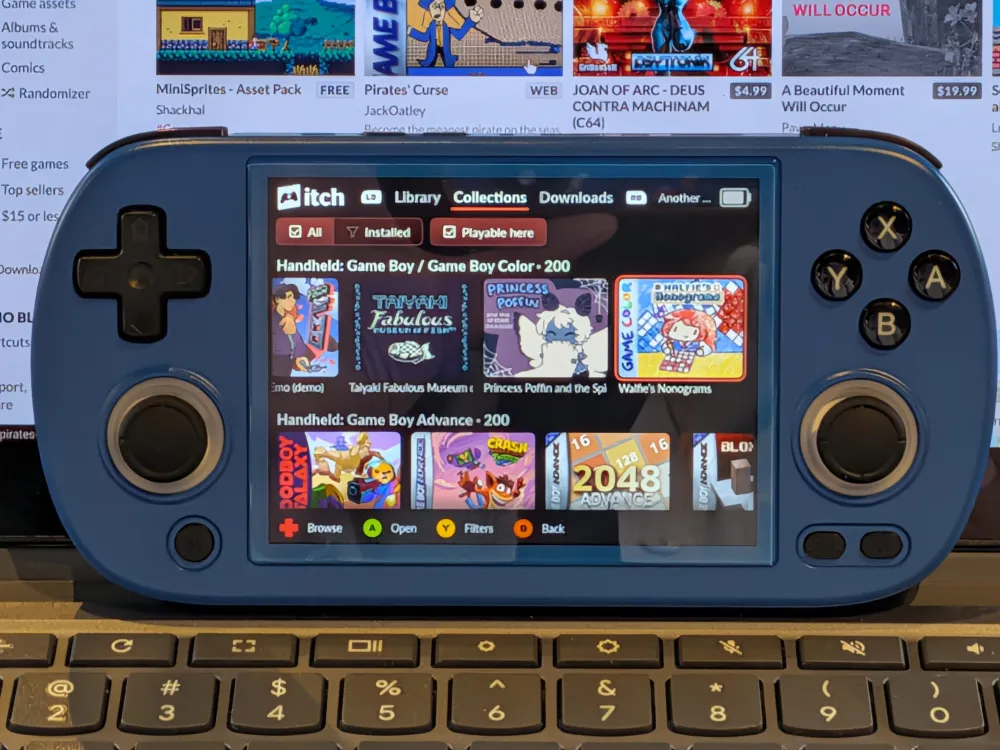
We’re working on (not so) secret project for Linux based handhelds. Maybe in the future we’ll expand this to android devices.

image.png

Admin

Of course, I’ll send you an email to your account’s primary email

Admin

Oh cool. I’m assuming you aren’t involved with the PortMaster version? I’ve just been testing games downloaded straight off of itch.io. If you’re interested at all I’d be glad to ship you an Ambernic RG40XX H for free. No pressure to do anything, but just in case you want to test your games on.

Admin

I would love to see a 4:3 compatible version of this game. I’ve been testing out Love games on pocket handhelds and this game is a lot of fun!

Admin

The warning only shows up if the link is embedding in another platforms iframe. Perhaps the method people are using to load your QR code is wrapping the game URL in something else?

Admin

We do, and we also published instruction on how to build your own client: https://itch.io/docs/butler/launcher-integration.html

Admin

Which description are you referring to? Can you give me page link examples

Admin

Thanks, fixed the link

Admin (2 edits)

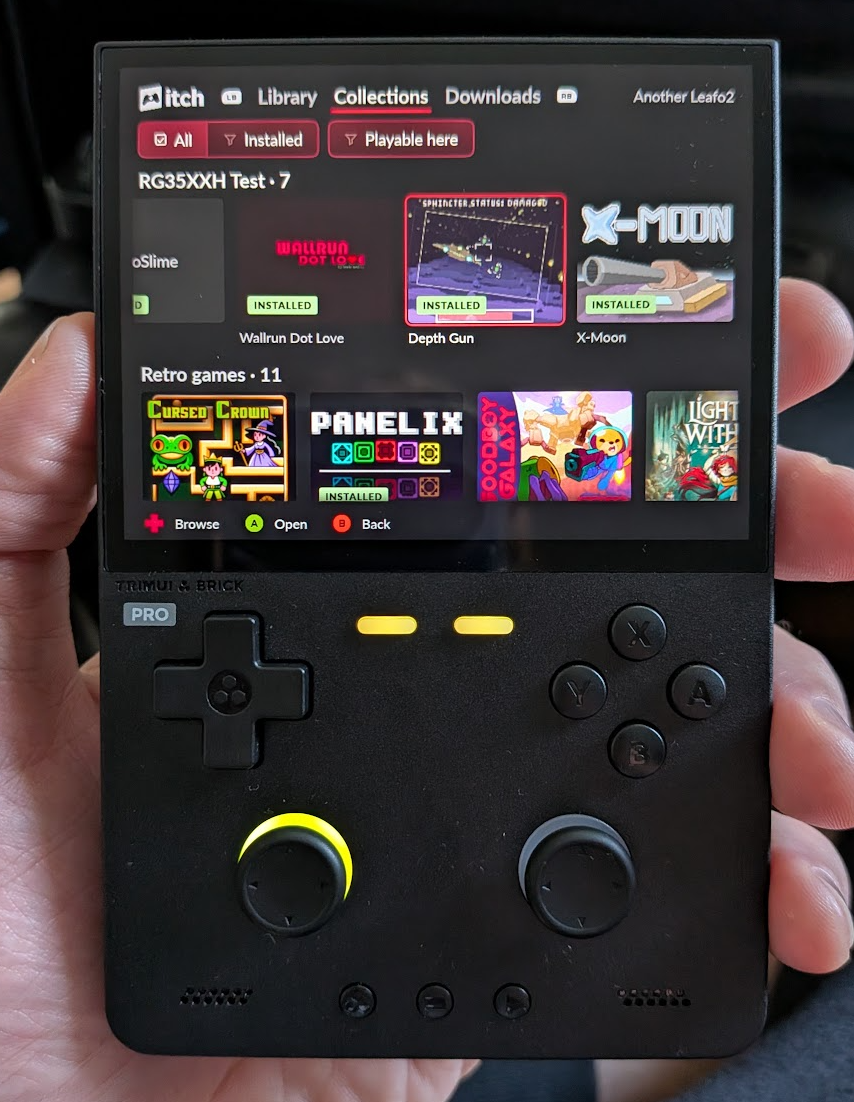
It’s a fun side thing, I don’t know how far I’ll take it. If you have muOS then you can try out the beta build via the .muxapp file here: https://github.com/itchio/zitch/releases

It supports retro roms, love2d games, and any native linux arm builds on sdl2

Admin

the difficulty needs to scale better in that mode, it’s too easy right now to be able to go forever. Thanks for playing!

Admin

Getting it ready for the itch deck

image.png

Admin (2 edits)

We have some updates for jam hosts today.

Jam Submission Requirements

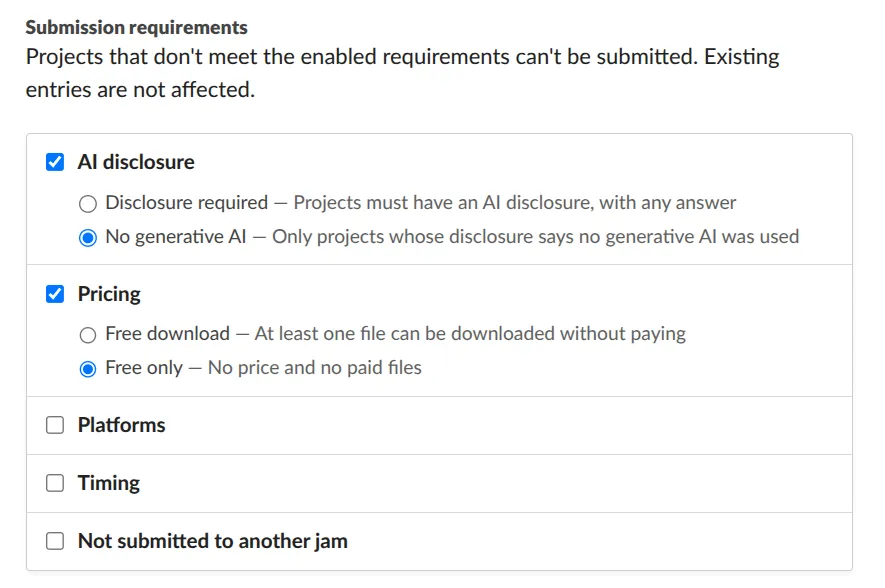
Jam submission requirements let jam hosts set a list of requirements a project must meet before it can be submitted. You’ll find them in the new Submission requirements section of the jam edit page.

Screenshot of Submission requirements

Here’s what’s available today:

  • Generative AI disclosure: Require entrants to fill out the generative AI disclosure on their project, or only accept projects that disclose no generative AI was used.
  • Pricing: Require a free download, meaning at least one file that can be downloaded without paying (demos of paid projects count), or only accept free projects with no price and no paid files.
  • Platforms: Require files for specific platforms: Windows, macOS, Linux, Android, or browser. You can accept projects with any one of the selected platforms, or require all of them. A platform counts when the project has at least one file for it, and browser means a playable HTML build.
  • Timing: Only accept projects created after the jam started, or projects whose first file was uploaded after the jam started.
  • Not submitted to another jam: Only accept projects that haven’t been entered in any other jam.

When someone submits, the submit dialog shows a checklist of the requirements for the selected project, and only projects that pass every requirement can be submitted. Requirements are checked at submission time, so changing them later does not affect existing entries.

Updated Field Editor

With this update, we’ve also re-implemented the fields editor for jams. As a reminder, fields allow you to collect additional information from participants along with their submission.

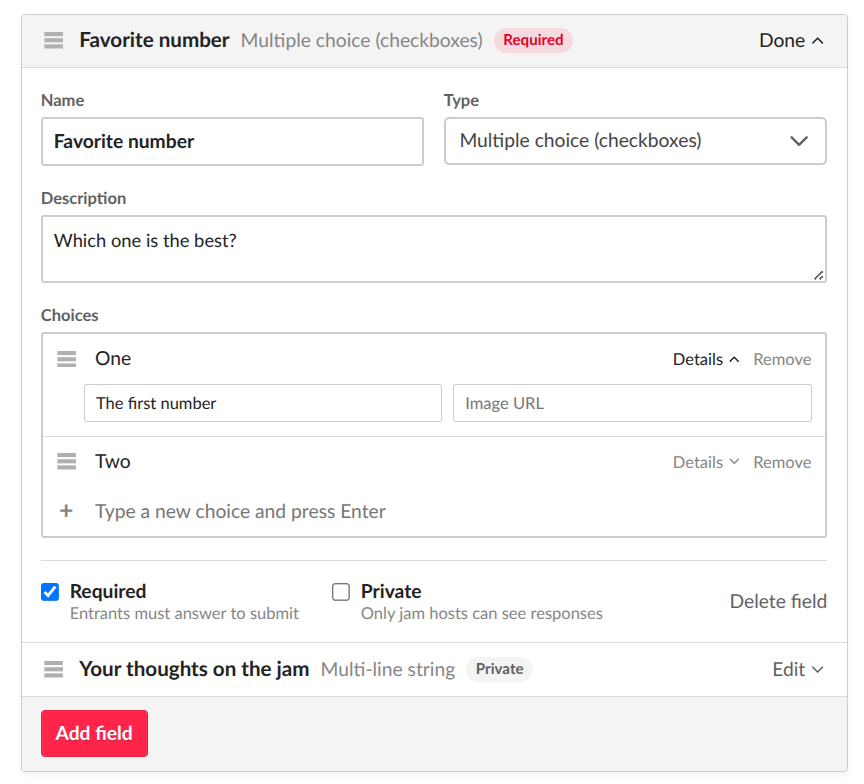
Field editor screenshot

The new editor allows you to easily edit the choices for single and multiple choice fields without having to manually write CSV. Anything that can be reordered also conveniently now has drag and drop handles. The field editor also collapses by default, so it’s easier to navigate the jam edit page once you’ve set up all of your fields.

If you have any more ideas for jam submission requirements please share them in this thread.

Thanks!

Admin

A little late… but now publishing a modern .love file that should work the most recent version of Love. Enjoy :)

Admin

It’s a bug caused by the poster who keep deleting and reposting to “bump” the topic. The number of deleted post rows hit a threshold where it broke pagination. I’ve reset the topic so that it should render again correctly as a short term fix for that topic. Thanks

Admin

“ai-assisted” is not a common tag that creators use, so the exclusion filter you are applied effectively does nothing. We apply a special “No AI” tag to pages where creators have specified their pages do not use generated AI. You can access it like this: https://itch.io/games/platform-web/tag-no-ai

Admin

Any “moderator” of the community/comment thread in question has the power to approve comments. itch.io may also approve comments in some scenarios.

We’re aware the UI/UX for approval is janky right, we’re working on unified page in your dashboard for comment approval across all communities moderated by that account.

Admin

Do all of them show up here? https://itch.io/my-purchases/bundles

Pinned ReplyAdmin

Mega bundles are now properly handled in the app. Please avoid running any scripts to hammer our server, there are only disadvantages as it can mess with how your account normally operates.

https://itch.io/updates/itch-app-bundle-support-launch-args-and-more

Pinned ReplyAdmin

We replaced how search works in the latest update: https://itch.io/updates/itch-app-bundle-support-launch-args-and-more

  • Autocomplete now only matches local projects by title
  • There’s a link to bring your search query up on the full site search

Sorry it was so janky for so long

Pinned ReplyAdmin

This has been addressed in the latest update: https://itch.io/updates/itch-app-bundle-support-launch-args-and-more